
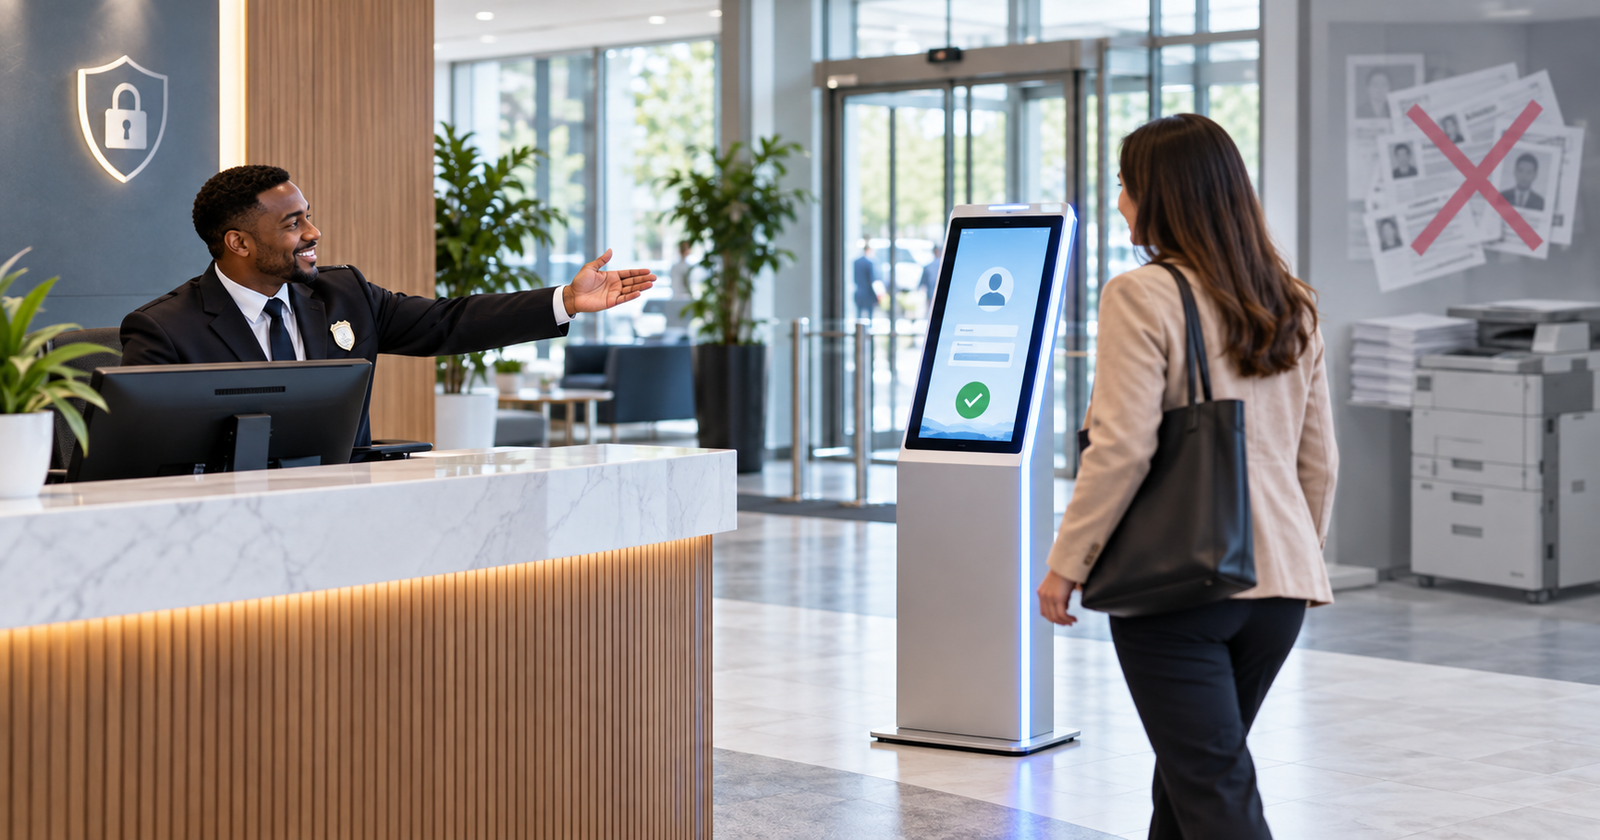
Walk into almost any factory gate, corporate tower, or warehouse in India and you will still find a spiral-bound register next to a photocopier. A visitor hands over an Aadhaar card, a driving licence, or a voter ID. The guard flips it over, runs it through the machine, staples the copy to a slip, and waves the person in. It feels thorough. It looks like due diligence. For fifteen years, nobody questioned it—until the arrival of the DPDP Act visitor management requirements made clear that this old habit could no longer stand.
That habit is now a liability, not because of some abstract compliance theory. India's Digital Personal Data Protection Act, 2023, and the DPDP Rules, 2025 changed the stakes. These rules were notified on 13 November 2025 and published in the Gazette a day later. They turn a stack of photocopied ID cards into a discoverable, attributable, and penalisable data set. Organisations get an 18-month compliance window, running until 13 May 2027. But the clock is already running, whether companies are ready or not. Most reception desks handle identity documents poorly today. This approach would not survive scrutiny, even under a generous reading of the law. Security teams that adopted DPDP Act visitor management workflows can finally log who moved a visitor's ID copy and when. Security heads who ignore DPDP Act visitor management obligations risk discovering, only after a breach notification deadline, that nobody can say which employee last handled a visitor's Aadhaar copy.
This article is written for the admin, HR, or security head who actually owns the front desk — not for lawyers. It is not legal advice, and you should treat it as a starting point for a conversation with your own counsel, not a substitute for one. What it will do is explain, in practical terms, why the photocopy pile is a problem, and what a defensible alternative looks like.
The old habit: photocopy first, ask questions never
The photocopy became standard practice because it felt like verification. A guard sees a face, sees a photo ID, sees they roughly match, and keeps a copy "just in case." Nobody defined in case of what. Nobody defined how long "just in case" lasts. Nobody defined who could later open that drawer and flip through hundreds of strangers' Aadhaar numbers, addresses, and photographs.
What actually happens to that photocopy
In practice, the paper trail looks like this:
- It sits in an open tray or unlocked drawer at the reception desk, visible to every other visitor waiting in the lobby.
- It gets bundled and moved to a storeroom once the tray fills up, with no log of who moved it or when.
- It is rarely destroyed on any schedule — registers and copy piles from three or four years ago are common in older factories and warehouses.
- Nobody can answer, on demand, "who has looked at this visitor's Aadhaar copy since it was collected?" Under DPDP Act visitor management expectations, storing Aadhaar photocopies in an unlocked drawer for years counts as indefinite retention without justification. The 18-month runway ending 13 May 2027 sounds generous, but any DPDP Act visitor management overhaul touching reception hardware, guard training, and retention schedules typically takes longer than admin teams assume.
None of this was illegal in the old regime because there was no operative law governing personal data handling in this specific way. That absence is over.
What changed: the DPDP Act and the 2025 Rules
The Act treats identity documents, phone numbers, and photographs collected at your gate as personal data, full stop. The Rules that operationalise it, notified in November 2025, add teeth in three places that matter directly to a reception desk.
Consent has to mean something
Consent under the Rules must be free, specific, informed, and unambiguous, communicated through a plain notice describing exactly what is being collected and why. A guard saying "ID please" while pointing at a photocopier is not that. Withdrawing consent also has to be as easy as giving it — which is nearly impossible to honour when the "consent" was a signature on a paper register you cannot easily retrieve or amend.
Retention is no longer optional silence
The Rules set a minimum retention period for personal data, traffic data, and logs. This period is at least one year after processing. A longer period applies if other laws require it. The Rules also require erasure once the original purpose has been served. A photocopy sitting in a storeroom for four years fails this test. There is no policy behind it, so it fails in both directions. It may be kept too long past its original purpose. There is also no proof of when the retention clock even started. We've written separately about [how long gate records should actually be kept](#) and how to build a defensible schedule around it. An 18-month runway sounds generous, but rewiring reception desks for DPDP Act visitor management means auditing every gate, tower, and warehouse before 13 May 2027. Under DPDP Act visitor management expectations, an unlocked drawer of photocopied ID cards is no longer just sloppy housekeeping — it's an unsecured personal data store with no access log.
Breach notification and penalties are real
If that storeroom floods, if a former employee walks out with a folder, or if a photocopy pile is found in a scrap dealer's shop — which has happened to registers and printed records at Indian sites before — the organisation is required to notify the Data Protection Board and the affected individuals. Penalties under the Act scale up to ₹250 crore per instance for the most serious failures. That number is not a rounding error for a mid-sized manufacturing unit or a business park operator.
Who is actually holding the risk
This is the part most facilities teams get backwards. If your company collects visitor ID data — on paper or digitally — your company is the Data Fiduciary. That is the entity accountable to the regulator and to the visitor. A software vendor whose platform you use to capture that data is a Data Processor, operating on your instructions. Switching from a paper register to a screen does not transfer the risk to the vendor; it stays with you. What a good vendor does is give you the tools to discharge that responsibility — audit trails, access controls, and a documented notice — rather than leaving you to invent them at the reception desk with a rubber stamp and a photocopier. The Ministry of Electronics & IT publishes guidance on personal-data handling that is worth bookmarking as the compliance deadline approaches, and it is a useful reference point independent of any vendor's marketing.
The specific problems with paper ID copies
Why DPDP Act Visitor Management Turns Photocopied IDs Into a Compliance Risk
Beyond the general retention and consent issues, paper photocopies fail on three practical points that a regulator, an auditor, or simply an anxious visitor will ask about.
No record of consent
A signature in a register does not prove the visitor was shown what would happen to their data, or that they understood it. There is no version history — if the notice on the back of the register page changed last year, you cannot prove which version a visitor from 2023 actually agreed to. Unlike a spiral-bound register, DPDP Act visitor management systems can enforce automatic purge schedules instead of letting copies pile up for three or four years. HR and facilities teams evaluating vendors should ask specifically whether a visitor kiosk was built around DPDP Act visitor management principles or merely repackaged as a digital photocopier.
No control over who sees it
Anyone standing at the desk, including other waiting visitors, can see an ID photocopy in an open tray. There is no role-based restriction. Compare that to how sensitive fields should be handled in any modern system, where ID images and phone numbers are visible only to roles that need them, as described on our /security page.
No way to reverse or track exports
If a photocopy is handed to the wrong department, photographed on a phone, or included in an audit pack by mistake, there is no undo. A digital record, by contrast, can be reversed with a documented reason rather than silently deleted, and every export can be tied to a person and a permission level.
What a compliant front desk looks like instead
The fix is not complicated, but it does require deliberately designing the check-in step rather than delegating it to whatever the guard finds fastest.
A visible, specific privacy notice at check-in
Each site should show visitors a plain-language notice at check-in. This notice should explain what data is collected, why, and for how long. The system should record that the visitor accepted this notice. It should also store a hash of the exact wording shown. This ensures the notice text cannot later be disputed. This is one area where VizPass stands out. Built for Indian offices, factories, and warehouses, it automates this process. VizPass records the acceptance timestamp and notice version on every pass. This happens automatically, rather than being left to memory. Because the DPDP Rules were gazetted on 14 November 2025, any front-desk process ignoring DPDP Act visitor management principles is now demonstrably out of step with the law. Because the DPDP Rules impose purpose limitation and storage duration on identity data, DPDP Act visitor management now requires reception desks to define exactly why an ID copy is kept and when it gets purged.
Role-based access to sensitive fields
ID images and phone numbers should not be visible to every user of the system. Receptionists checking someone in do not need the same visibility as a compliance officer pulling a monthly audit. Structuring roles this way is standard practice across the /industries VizPass serves, from manufacturing campuses to multi-tenant business parks.
Reversible records and controlled exports
Records should never simply vanish, and they should never be freely downloadable by anyone with desk access. Exports should require permission, and any correction to a visitor record should be logged with a reason rather than overwritten. It is also worth knowing where that data physically sits — for Indian workplaces this is usually a question of hosting location, and details on where records are stored are covered on our /data-hosting-and-residency page.
One caveat worth stating plainly
No platform can currently promise to automatically purge records the moment a retention period lapses without human review — that kind of fully automatic retention purge is not yet standard, VizPass included, and any vendor claiming otherwise for a live production system should be questioned closely. Build a manual review cadence into your compliance calendar until that maturity exists.
Practical steps for this quarter
- Pull every register and photocopy pile currently in storage and date it — you cannot set a retention policy on records whose age you don't know.
- Draft one plain-language visitor notice per site and get it displayed at the point of entry, not buried in an HR policy PDF nobody reads.
- Decide, in writing, who at your organisation is allowed to view ID images and phone numbers, and who is only allowed to view names and timestamps.
- Stop photocopying ID cards as a default. If a factory floor genuinely requires ID capture for safety or regulatory reasons — worth checking against DGFASLI's guidance on factory safety obligations — capture it digitally with a logged notice, not on paper.
- Review your current visitor process against the checklist in our piece on the six visitor policies every gate should have, and compare it with what a paper register fundamentally cannot tell you.
Conclusion
The photocopy at reception was never really about security — it was about being seen to do something. Under the DPDP Act and the 2025 Rules, "something" now has to be specific, documented, and defensible: a notice the visitor actually saw, a consent record you can produce, access limited to the roles that need it, and a retention policy you can explain to a regulator without guessing. If your current process is a guard, a photocopier, and a drawer, the honest next step is to see how a structured check-in flow — like the one available across VizPass's /features — handles consent, roles, and exports before your 18-month compliance window gets shorter. Book a walkthrough at /contact and bring your current register with you; it's the fastest way to see exactly where the gaps are.